Tuesday evening, my phone buzzes. It’s a founder from Noida, and he’s already mid-sentence before I say hello. Customer data has leaked from some bulk SMS tool his team uses. About 40,000 phone numbers, he thinks. He’s angry, properly angry, at the vendor.
“Their server, their problem. Why should I be answerable?”
I let him finish. Then I told him what I’m about to tell you, because this one misunderstanding sits under almost every data fiduciary vs data processor question I get.
Who’s Who in Data Fiduciary vs Data Processor
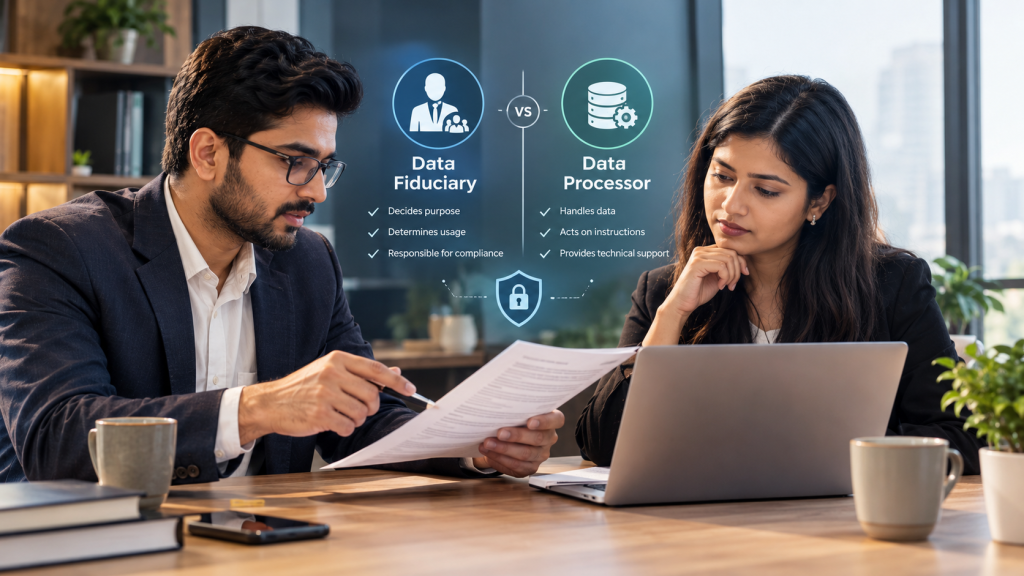
The Data Fiduciary is whoever decides why the data is collected and what happens to it. If you run the shop and you own the customer, that’s you. The Data Processor just does a job with that data because you told them to. Your SMS tool, your cloud host, your payroll software, the call centre in Gurugram that phones your customers.
Ask yourself who wanted this data in the first place. Whoever that is, is the fiduciary.
Roles aren’t fixed either. A payroll company is a fiduciary for its own employees and a processor for every client’s employees. Same office, same people, two different hats depending on whose data you’re looking at.
Why the Blame Lands on the Fiduciary
Back to the Noida call. Under the DPDP Act the Data Fiduciary stays responsible for compliance, even if a processor does all the actual handling. Giving data to a vendor doesn’t give away the responsibility. I wish it did. It would make my job easier.
The Act also expects a valid contract before you bring a processor on board. An email quote doesn’t count, and neither does “we’ve worked together for years.” And you’re still expected to keep reasonable security safeguards in place, which covers what your vendor does too.
So when that data leaked, the first person the regulator would want to hear from was my caller. Not the SMS company. His customers had trusted him with their numbers, not the vendor.
He went quiet for a bit. Then he said, “So what do I do now?”
What Your Contract With a Processor Needs to Say
Honestly, this is where I see the biggest holes. Most vendor agreements I read are about price, uptime and payment dates. Data protection gets one line, if that. I’ve covered the full detail in my guide to data processing agreements under the DPDP Act, so I’ll just give you the short list here.
Say exactly which data the vendor can touch, and for what. Put a deadline on telling you about a breach. Don’t let them pass your data to sub-vendors without your approval. Decide what happens to the data when the contract ends. And write down who pays if their mistake costs you money, because someone will have to.
If your contracts say nothing about any of this, you’re carrying risk you never priced in.
When Two Companies Are Both Fiduciaries
This one’s less common but it bites harder. Picture a retail brand running a loyalty card with a partner bank. Both sides decide how the customer data gets used. Neither is simply working for the other. Both can end up being fiduciaries, with duties on each side.
If you’re in a setup like that, sit down and write out who does what. Who replies when a customer asks for their data? Who reports a breach? Who updates the privacy notice? Loose arrangements work fine until the first complaint arrives.
An Hour of Homework
Open a spreadsheet. List every vendor that sees customer or employee data. Next to each one, mark whether they’re your processor or a fiduciary in their own right. Then ask three things. Is there a signed contract? Does it say anything real about data protection? Do you even know where your data is stored?
Almost everyone I’ve done this with finds two or three gaps in the first hour. That’s normal. It’s also fixable, which is the good news. If you’re unsure who should handle customer complaints about vendor mistakes, our post on grievance officers under the DPDP Act is a decent place to start.
Read the Actual Text
The definitions and duties are in the Act itself, so go to the source. The Ministry of Electronics and Information Technology publishes the Act and the rules. They get amended now and then, so check the latest version before you rewrite any contract.
Sort It Out on a Calm Day
Understanding the data fiduciary vs data processor line isn’t a law-school exercise. It decides who gets blamed, who pays, and who sits across from the regulator. Much better to work that out on an ordinary Tuesday than in the middle of a breach.
The Noida founder, by the way, spent two weeks fixing contracts he should’ve fixed a year earlier. Don’t be him. If you’re not sure where your vendors stand, book a free consultation and we’ll go through the list together.