If you run a website in India, you have probably copied a cookie banner from somewhere. It says “We use cookies. Accept.” Most sites stop there.
Under the Digital Personal Data Protection (DPDP) Act, 2023, that one-button banner is unlikely to survive scrutiny. It also doesn’t take much to fix.
Here is what the law requires, what it doesn’t, and what your website should do before the deadline.
First, a Myth: “The DPDP Act Doesn’t Mention Cookies”
That is true. The Act never uses the word “cookies”. But it doesn’t need to.
The DPDP Act applies to any digital personal data. Cookies, device IDs, advertising IDs and IP addresses often identify a person or can be linked to one. If your website uses them for analytics, retargeting or personalisation, you are a Data Fiduciary, and the visitor is a Data Principal.
So the real question is not “does the DPDP Act cover cookies?” It is “are my cookies collecting personal data?” For most websites running Google Analytics, Meta Pixel or similar tools, the answer is yes.
When Does This Become Enforceable?
The DPDP Rules, 2025 were notified in November 2025 with a phased rollout. The Data Protection Board provisions took effect immediately, the Consent Manager provisions apply after one year, and the rules on notice, verifiable consent, security safeguards and breach reporting apply after 18 months. That last date falls on 13 May 2027. mondaqmondaq
Treat this as a build window, not a grace period. Consent logs, banners, vendor contracts and privacy notices all take time to fix.
What Counts as Valid Consent?
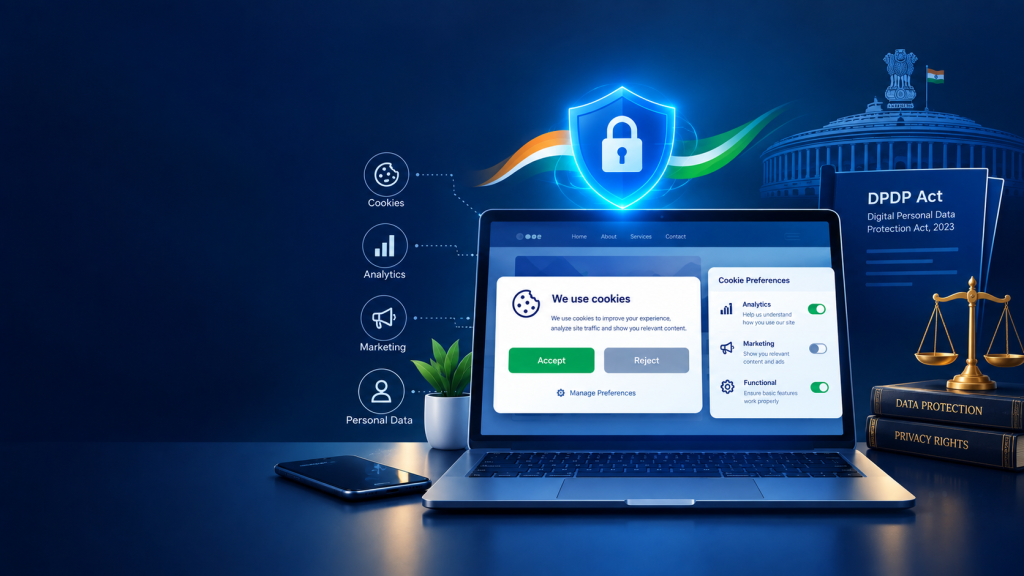
Under the Act, consent must be free, specific, informed, unconditional and unambiguous. It must also be given by a clear affirmative action. In practice, a cookie banner should have the following.
1. No pre-ticked boxes and no tracking before consent.
Non-essential cookies (analytics, marketing, third-party pixels) must not fire until the visitor opts in. Silence, scrolling or continued browsing is not consent.
2. A real choice.
“Accept All” and “Deny” (or “Reject All”) should be equally visible. Hiding the reject option behind “Manage Preferences” is a dark pattern, and it weakens the “free” and “unambiguous” test.
3. Granular purposes.
Let users choose by category: functional, preferences, statistics and marketing. Bundling everything into one consent is not specific consent.
4. A clear, standalone notice.
The notice should be in plain language. It should list what data is collected and for which purpose, explain how to withdraw consent, and tell the user how to exercise their rights and complain to the Data Protection Board. The Act also gives users the right to access the notice in English or any of the 22 languages in the Eighth Schedule of the Constitution.
5. Withdrawal as easy as giving.
If it took one click to accept, it should take one click to withdraw. Keep a persistent “Manage Consent” or “Cookie Settings” link in the footer.
6. Proof of consent.
The burden of proof is on you. Log what the user consented to, when, and which version of your notice they saw. If you cannot show this, you cannot defend it.
Do You Need Consent for Every Cookie?
No. Strictly necessary cookies, such as session cookies, security cookies and shopping cart cookies, are needed to deliver the service the user asked for. These generally don’t need opt-in consent, though you should still disclose them in your notice.
Everything beyond that, including analytics, ad tracking, social media pixels and behavioural profiling, should be consent-based.
Special Warning: Children’s Data
If your website serves users under 18, such as an EdTech or gaming site, the rules are stricter. The Act requires verifiable parental consent and prohibits tracking, behavioural monitoring and targeted advertising directed at children. If minors may visit your site, review your marketing pixels first.
The Website Compliance Checklist
Use this as a working list:
- Audit every cookie and tracker on your site, including those added by plugins and third-party scripts
- Classify each as necessary, functional, analytics or marketing
- Block non-essential cookies until the user opts in
- Show Accept and Reject buttons with equal prominence
- Replace vague banner text with purpose-specific wording
- Update your Privacy Policy and Cookie Policy to match the DPDP Act
- Add a “Manage Consent” link that stays accessible on every page
- Store consent records with timestamps and notice versions
- Review data processing agreements with Google, Meta, CRM and email vendors, because you remain responsible for processors acting on your behalf
- Prepare a process for access, correction, erasure and grievance requests
- Prepare a breach response plan
What Are the Penalties?
The Act provides for penalties of up to ₹250 crore, for example for failing to maintain reasonable security safeguards. Failing to notify a breach or mishandling children’s data can also attract penalties of up to ₹200 crore. Small businesses won’t see penalties at the maximum level in practice, but regulatory scrutiny and reputational damage can hurt a growing brand either way.
Common Mistakes We See
- Banners that only say “OK” or “Accept”
- Analytics and ad pixels loading before the user clicks anything
- A Privacy Policy copied from a template, with no DPDP-specific content
- No way to withdraw consent
- No record of consent
- Forgetting that contact forms, newsletter popups and chat widgets also collect personal data and need their own notice and consent
Final Thoughts
A DPDP-compliant cookie banner is not complicated, but it must be deliberate. Know what your website collects, ask for permission clearly, and keep proof. The sites that start now will not be scrambling in 2027.
If you are not sure whether your website meets these requirements, our DPDP Act compliance consulting team can run a gap assessment. You can also read our DPDP Compliance Cost Guide or book a free consultation.
Disclaimer: This article is for general information and is not legal advice. Please consult a qualified advocate for your specific situation.