A founder messaged me a few weeks ago after reading yet another compliance update. “Nitin, everyone keeps saying ‘consent manager’ like I’m supposed to know what that means. Do I need to build one? Hire one? Buy one?”
Fair question. And an increasingly urgent one, because the Consent Manager framework is one of the first parts of the DPDP Act to actually go live, with obligations phasing in around November 2026. If you run a business that collects personal data online, this is worth fifteen minutes of your attention now, not a scramble later.
What Is a Consent Manager, Exactly?
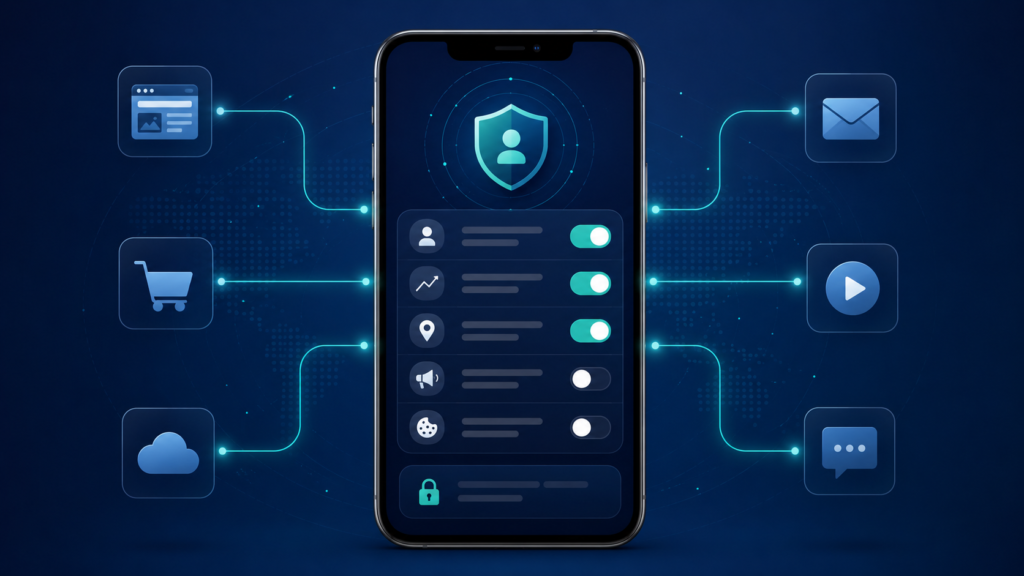
Under the DPDP Act, a Consent Manager is a registered, independent entity that acts as a single point through which a person (a “Data Principal”) can give, manage, review, and withdraw consent for how their personal data is used — across multiple companies, all from one dashboard.
Think of it a bit like an account-aggregator model, but for personal data consent instead of financial data. Instead of every website having its own separate, often confusing consent pop-up, a Consent Manager is meant to give individuals one interoperable place to control what they’ve agreed to, and with whom.
Consent Managers themselves must:
- Be registered with the Data Protection Board of India
- Meet technical, financial, and operational standards set by the government
- Act only on the instructions of the Data Principal, not the company collecting the data
- Maintain records of consent that can be verified and audited
Does Your Business Need to Be a Consent Manager?
For almost every business reading this — no. Being a registered Consent Manager is a specific, regulated role, generally taken up by fintech-style platforms or dedicated compliance infrastructure providers, not by an ordinary D2C brand, SaaS company, or clinic.
The real question isn’t “should we become a Consent Manager.” It’s:
“Is our consent process ready to plug into this ecosystem once it’s live?”
What This Actually Means for Most Businesses
Even if you never register as a Consent Manager, the framework changes what’s expected of your consent collection:
1. Your consent requests need to be granular, not bundled. “I agree to Terms & Privacy Policy” as one checkbox won’t hold up. Consent has to be specific to each purpose — marketing emails, analytics, third-party sharing — and each of these needs to be separately revocable.
2. Withdrawal has to be as easy as giving consent. If someone can opt in with one click, they need to be able to opt out with roughly the same effort. Burying withdrawal behind a support email or a multi-step form is a compliance gap.
3. Your systems need to actually respect withdrawal — not just log it. Once a Consent Manager (or a direct request) signals a withdrawal, your internal systems, vendors, and marketing tools need to stop processing that data. This is often the hardest part technically — plenty of companies can capture a withdrawal request but have no automated way to act on it across their CRM, email tool, and analytics stack.
4. Your Privacy Policy language needs to be interoperable-ready. As Consent Manager platforms roll out, they’ll expect standardised, machine-readable descriptions of what you’re asking consent for. A vague, lawyer-dense privacy policy paragraph won’t translate well into that system.
Why November 2026 Specifically?
The DPDP Rules, 2025 set out a phased rollout. Foundational provisions took effect immediately on notification in November 2025. Consent Manager registration and related obligations are the next major milestone, roughly a year later, ahead of full substantive compliance expected by May 2027.
Practically, this means the infrastructure around consent — how it’s collected, stored, and revoked — is what regulators and the market will be watching first. Getting your consent architecture right now avoids a rebuild later.
A Simple Way to Check Where You Stand
Ask yourself honestly:
- Can a customer see, in one place, everything they’ve consented to with us?
- Can they withdraw one type of consent (say, marketing) without withdrawing everything?
- If they withdraw, does that actually stop our email tool, our CRM, and our analytics from using their data — or just our own database?
- Is our Privacy Policy written in a way that maps cleanly to distinct, separable purposes?
If two or more of these make you pause, it’s worth getting a proper consent audit done before the framework goes fully operational.
We Can Help You Get Consent-Ready
We work with startups, SMEs, and growing businesses to audit consent flows, rebuild Privacy Policies around DPDP-compliant purpose separation, and prepare for Consent Manager interoperability — before it becomes a scramble.